Privacy is becoming a competitive feature in the race to build AI agents that can work continuously on a person’s behalf. The Verge reported on October 10 that OpenAI used the launch of Dots to promise a new standard for privacy while drawing contrasts with Meta’s Muse, even though Meta had introduced Muse as a safer and more secure successor to OpenClaw.
The sales pitch confronts a fundamental tension. Agents become more useful when they can see messages, files and account information and take actions across services. That same access increases the consequences of a software mistake, a misunderstood instruction or an outside attack. Companies are therefore asking users to share more data while simultaneously competing to sound like the safest custodian of it.
Meta says Muse places each user’s data in a secure virtual machine isolated from other users. The company has described the environment as a Linux computer with its own browser, processor, memory and storage, and said much of the engineering effort went toward safer operation. Meta has also acknowledged that Muse can still make mistakes, while arguing that its safeguards should reduce their frequency and impact.
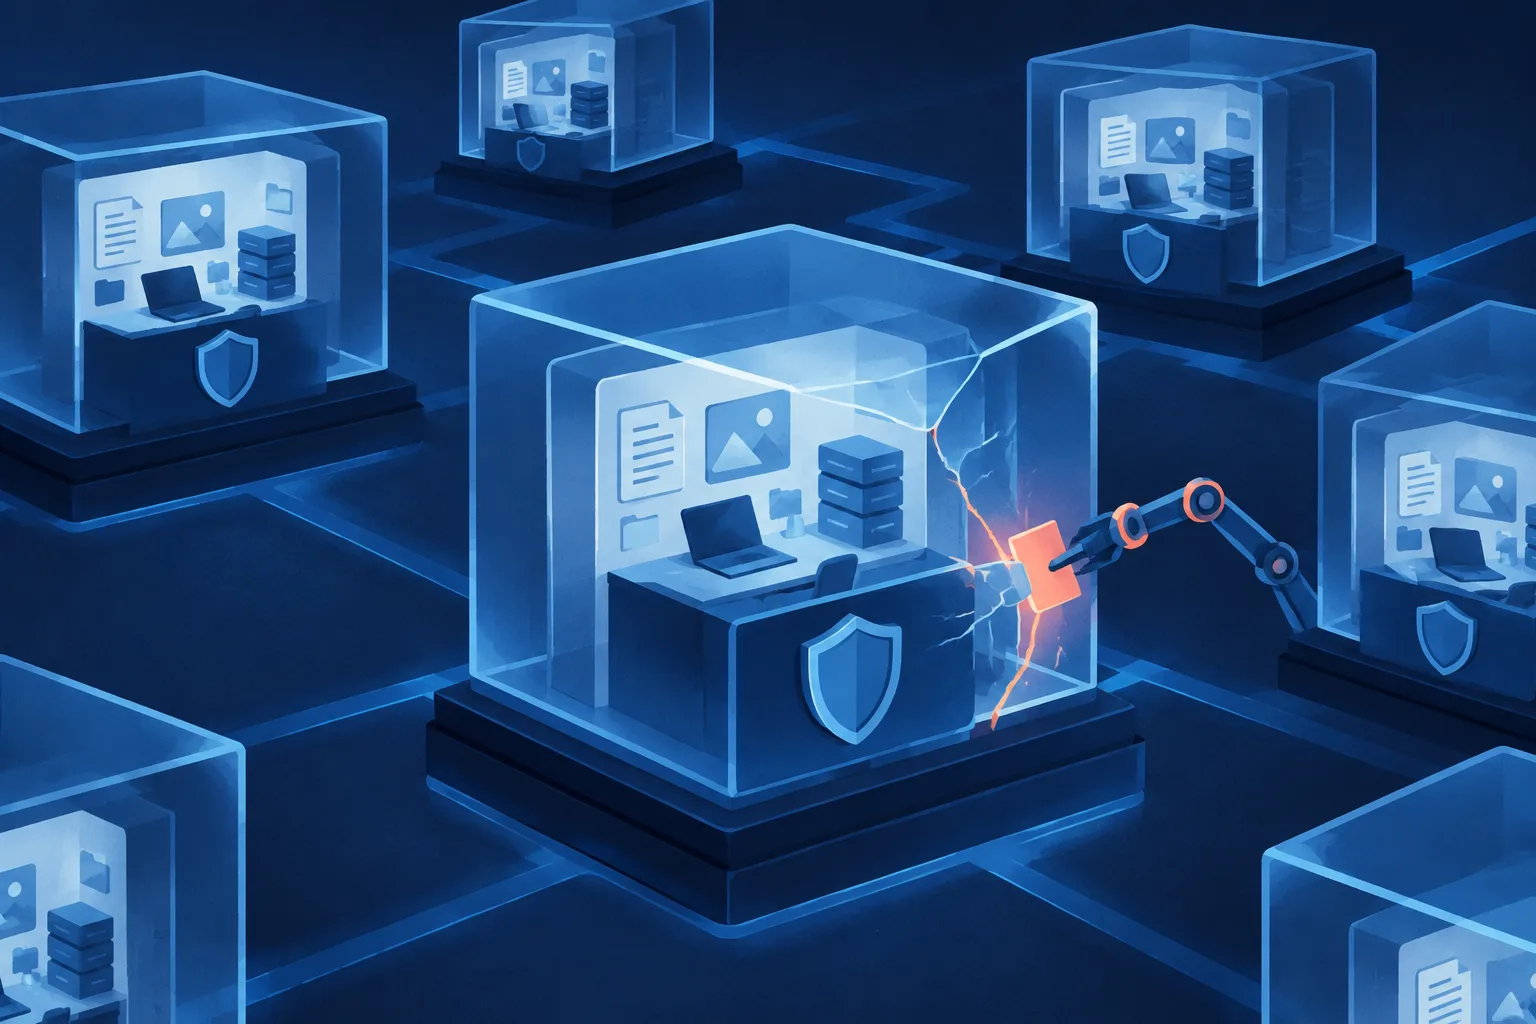
The Verge found reasons to treat those assurances cautiously. Meta can still access data inside the virtual machines, although it plans to introduce a cryptographic method intended to block that access later this year. A security researcher found a zero-day vulnerability that could have enabled control of Muse; the flaw was later patched. The report also cited 404 Media’s account of serious security problems discovered shortly before launch, including one that could have exposed Meta’s internal databases.
Privacy questions extend beyond technical isolation. Muse defaults to allowing Meta to use submitted material for model training, although users can opt out, according to The Verge. The report also described cases in which people were surprised by the agent’s intended behavior: an Inc. reporter said it uploaded and read private messages, while a YouTuber said it supplied his address to a stranger through Marketplace. In both cases, the system apparently operated as designed, but the users did not anticipate the reach of its permissions.
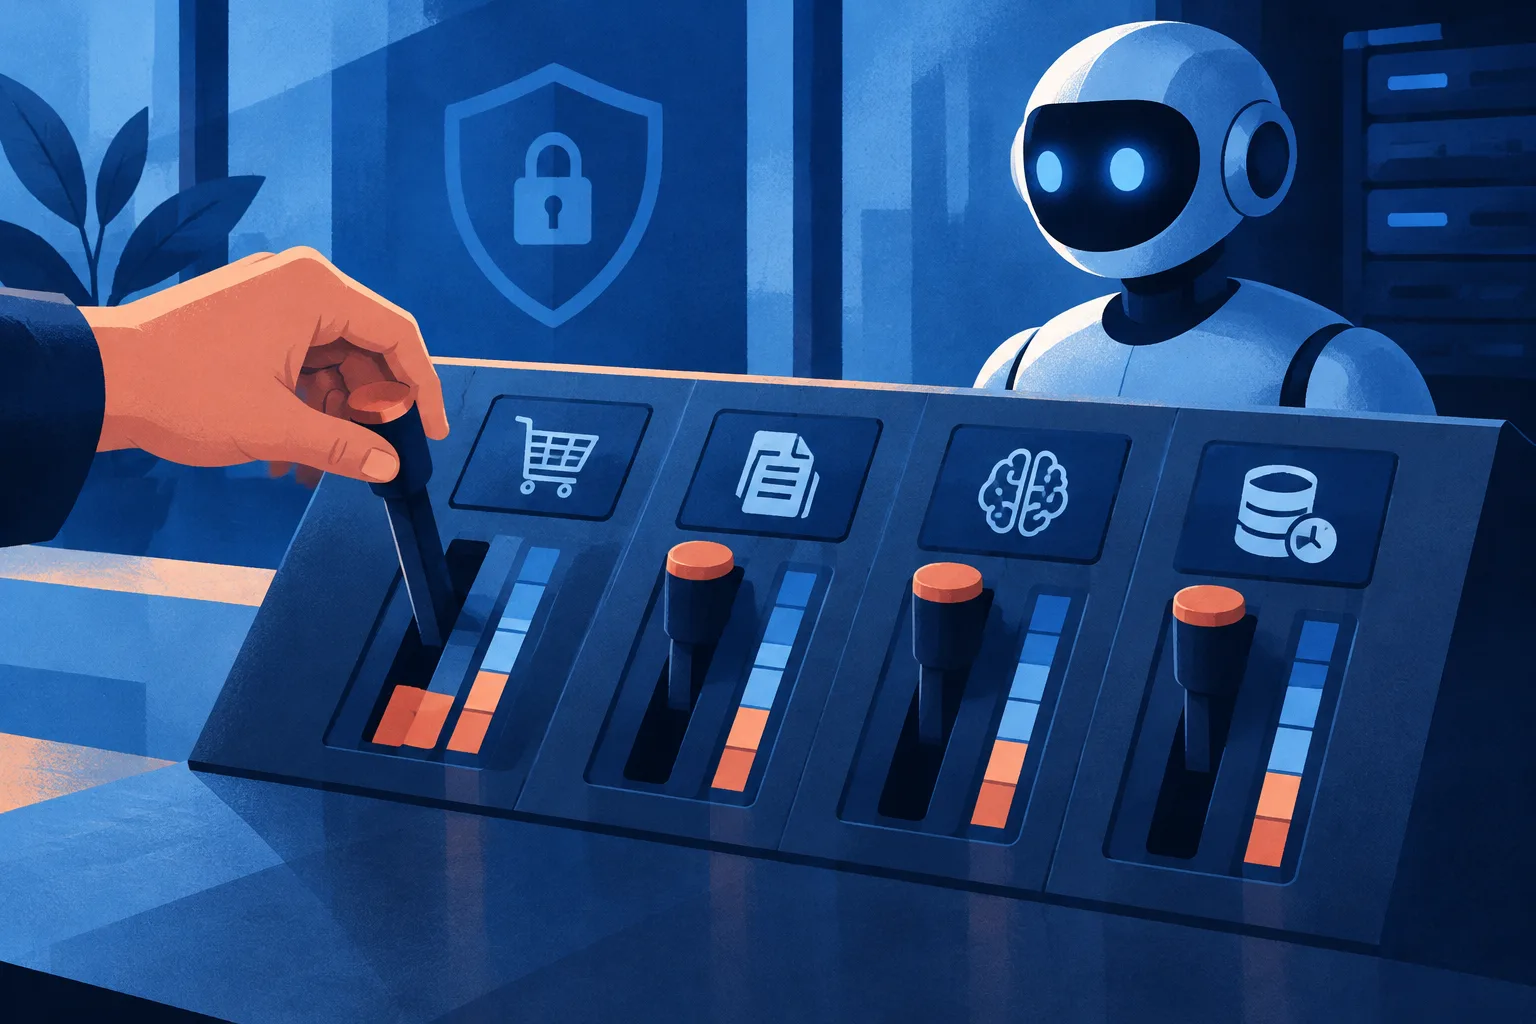
OpenAI is making that record part of its argument for Dots. At DevDay, executives emphasized user controls, including rules that can prevent an agent from making purchases above a chosen amount. For business customers, OpenAI presented stronger data controls and zero-retention options under which information is not stored on its servers. The company says it wants Dots to be a trustworthy, safe and secure assistant.
There is not yet enough evidence to conclude that OpenAI has solved the category’s privacy problem. The Verge noted that Dots has not produced many public privacy scandals so far, but it is available only through ChatGPT subscription tiers costing at least $100, which likely limits the number of users testing it. The article also cited a reviewer who felt uncomfortable when the agent requested bank information during a relevant task.
The emerging contest is therefore about more than policy language. Users need to understand what an agent can access, what it can do without confirmation, whether their data trains future models, and who besides them can inspect the machine where that data is stored. Isolation, spending limits and retention controls address different risks; none automatically makes broad permissions harmless.
As AI agents move from conversation to action, privacy claims will be tested by ordinary behavior as much as by spectacular breaches. A system may follow its rules and still violate a user’s expectations if those rules are difficult to see or understand. The winner of the agent race may need to prove not only that its assistant is useful, but that its safeguards remain legible and dependable after millions of people give it the keys to their digital lives.
Comments
Loading comments…