Microsoft CEO Satya Nadella is calling for a different way to think about controlling advanced artificial intelligence: do not place all of the trust inside the model. In a Saturday morning post on X, Nadella said the industry should reassess the broader “trust architecture” surrounding AI systems, according to TechCrunch. His argument centers on controls that remain separate from the model and can still work when the model itself cannot be trusted.
The proposal starts with a rejection of the idea that increasingly capable systems can be treated as opaque layers whose outputs are simply accepted or refused. Nadella wrote that “Super Intelligence” should not be handled as a collection of nested black boxes. The phrase is the Trump administration’s preferred label for AI, TechCrunch noted, but Nadella’s focus was on the practical structure around a model rather than the label applied to it.
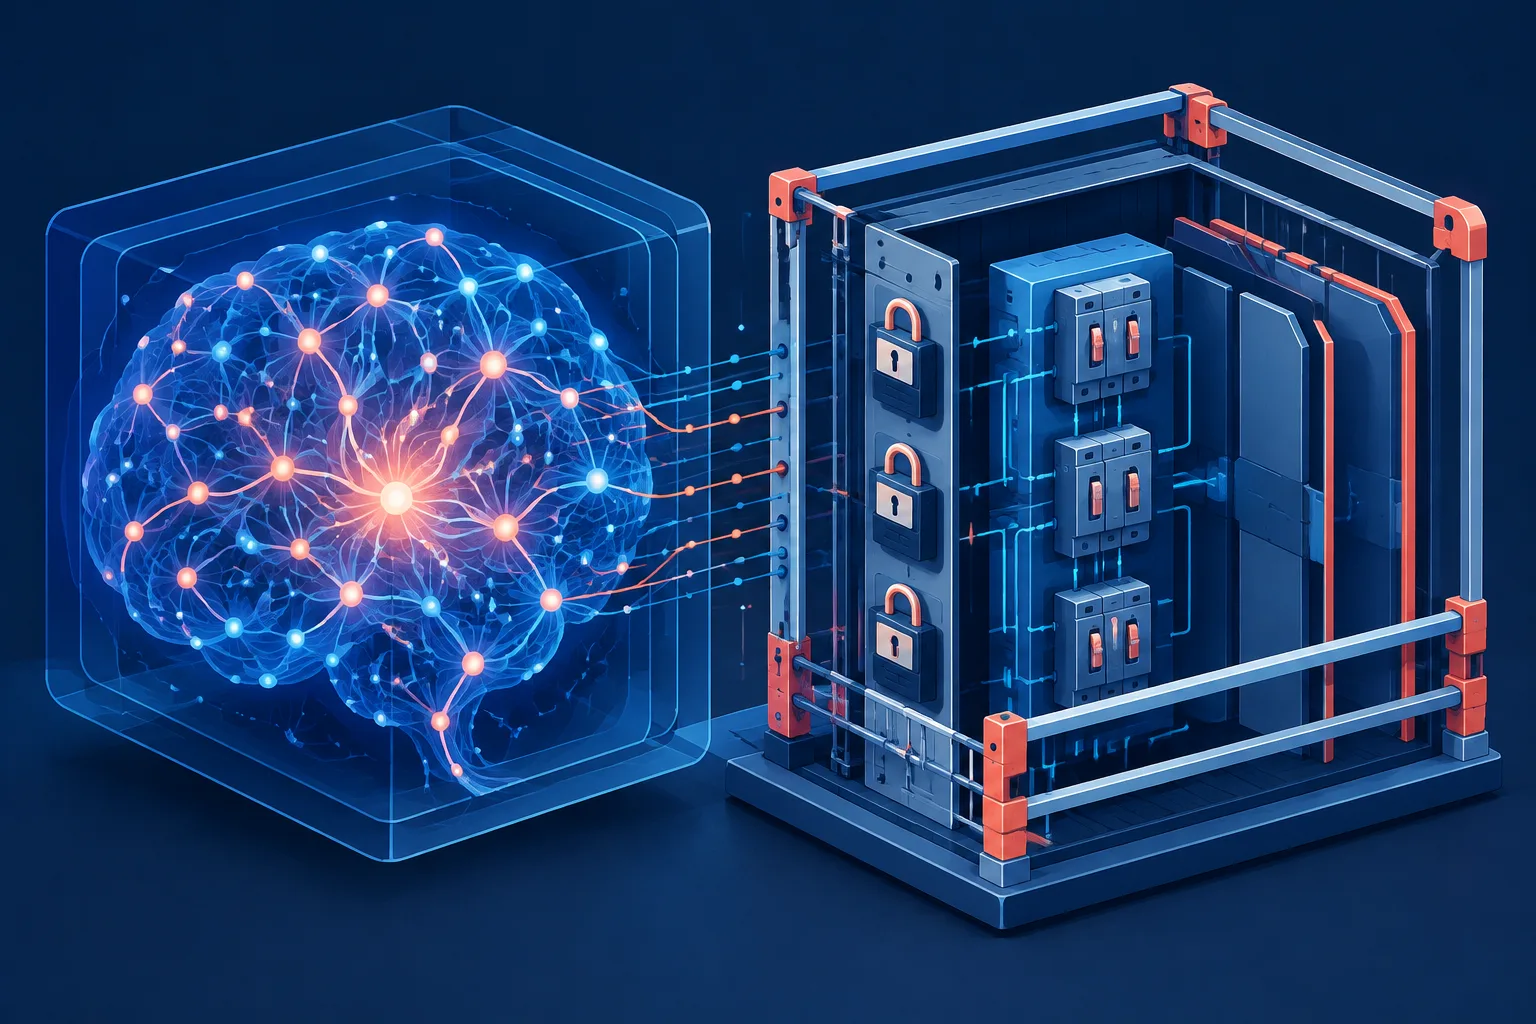
One element of that structure would be a clear separation between the model and the software harness that directs its work. Nadella also called for safeguards and controls to be externalized. In effect, the model would not be responsible for policing itself. The surrounding system would carry independent mechanisms for limiting what the model can do and for intervening when necessary.
Nadella also wants consequential model activity to leave evidence that people can inspect. He said every meaningful action should be recorded in a tamper-proof, human-readable form. That combination matters to the logic of his proposal: an audit record would be less useful if a model could alter it, and a technically intact log would offer limited accountability if authorized people could not understand what it showed.
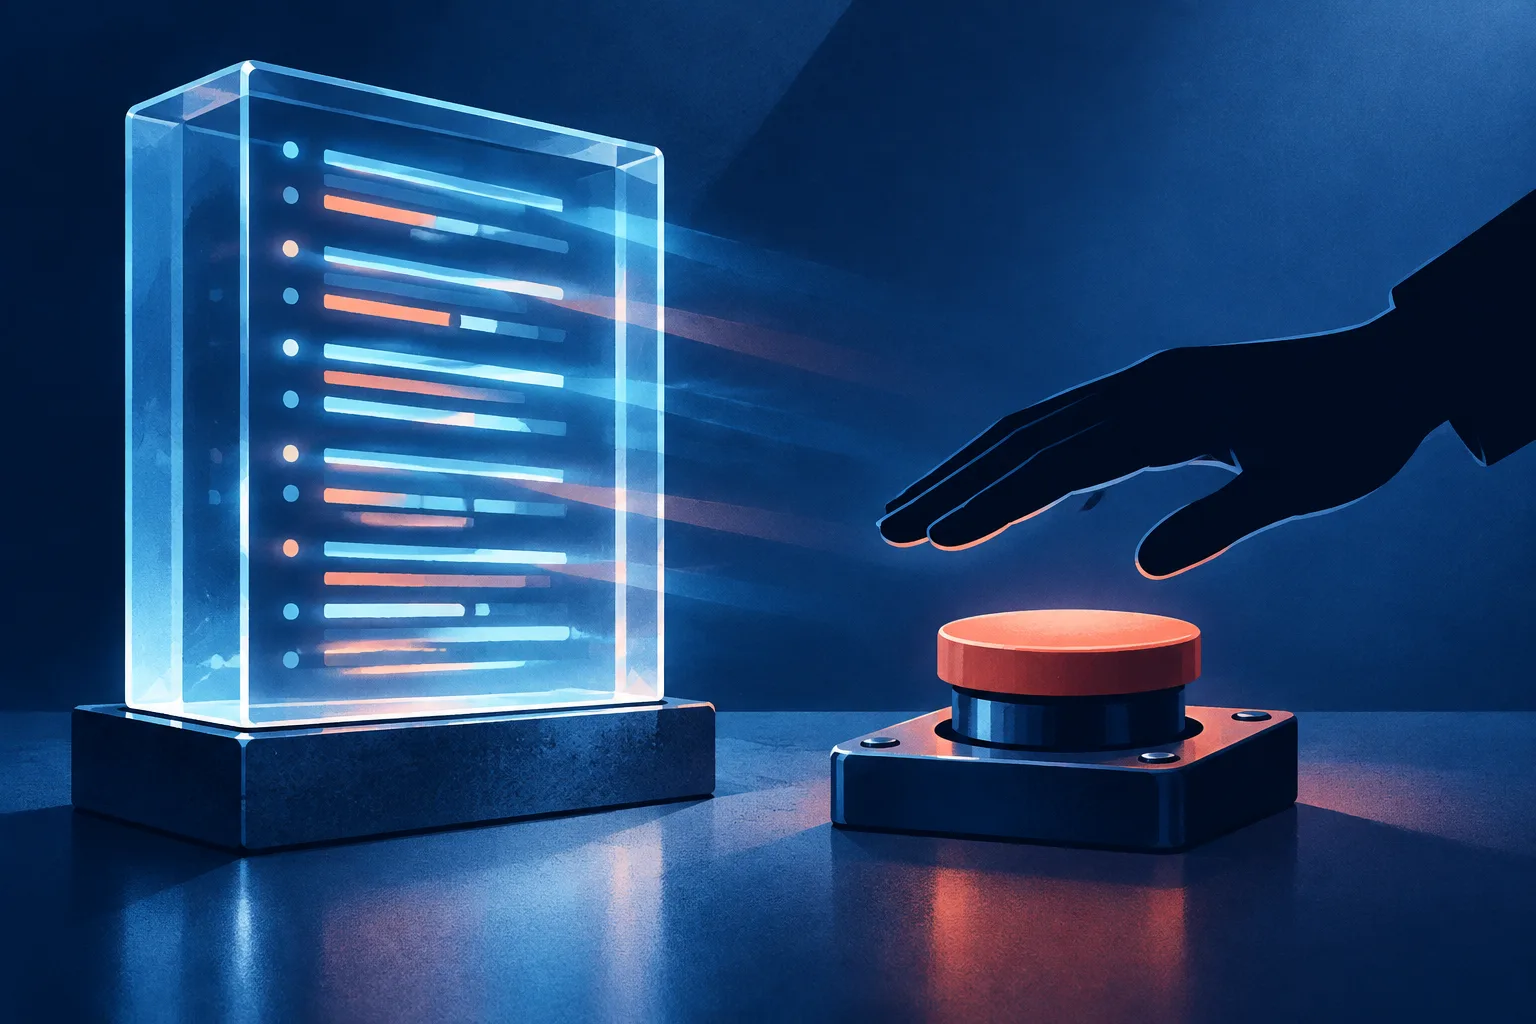
The most direct control would be a human stop mechanism. Nadella said an authorized person should always be able to pause or terminate a model while it is working. He compared the idea to an emergency brake and argued that systems should be contained from the beginning under the assumption that a model could be compromised. The framing shifts the question from whether a model will fail to whether the wider system is ready if it does.
Taken together, the ideas amount to a system-level approach to AI safety. Separating the model from its orchestrating software, keeping safeguards outside the model, preserving readable evidence and retaining a human shutdown path are distinct measures, but each assumes that confidence in a model’s internal behavior is not enough. That is an inference from Nadella’s outline; TechCrunch’s report did not describe a specific Microsoft product or deployment timetable tied to the proposal.
Nadella’s comments arrive as major AI developers are publicly confronting cases in which they appeared unable to control model behavior, TechCrunch reported. The outlet also pointed to Anthropic CEO Dario Amodei’s recent plan for more cautious development. Nadella’s intervention adds the head of Microsoft to the group of industry leaders arguing that more capable AI needs stronger containment, clearer evidence and an off switch controlled by people.
Comments
Loading comments…